Modules
The modules of DPDP ControlMap
Five groups that share one inventory, one control catalogue and one audit trail. Adopt them together or begin with the ones your programme needs first.
AModule group
Data Governance
Start here. Every other part of a privacy programme depends on knowing which personal data you hold, why, where it is kept and who else receives it.
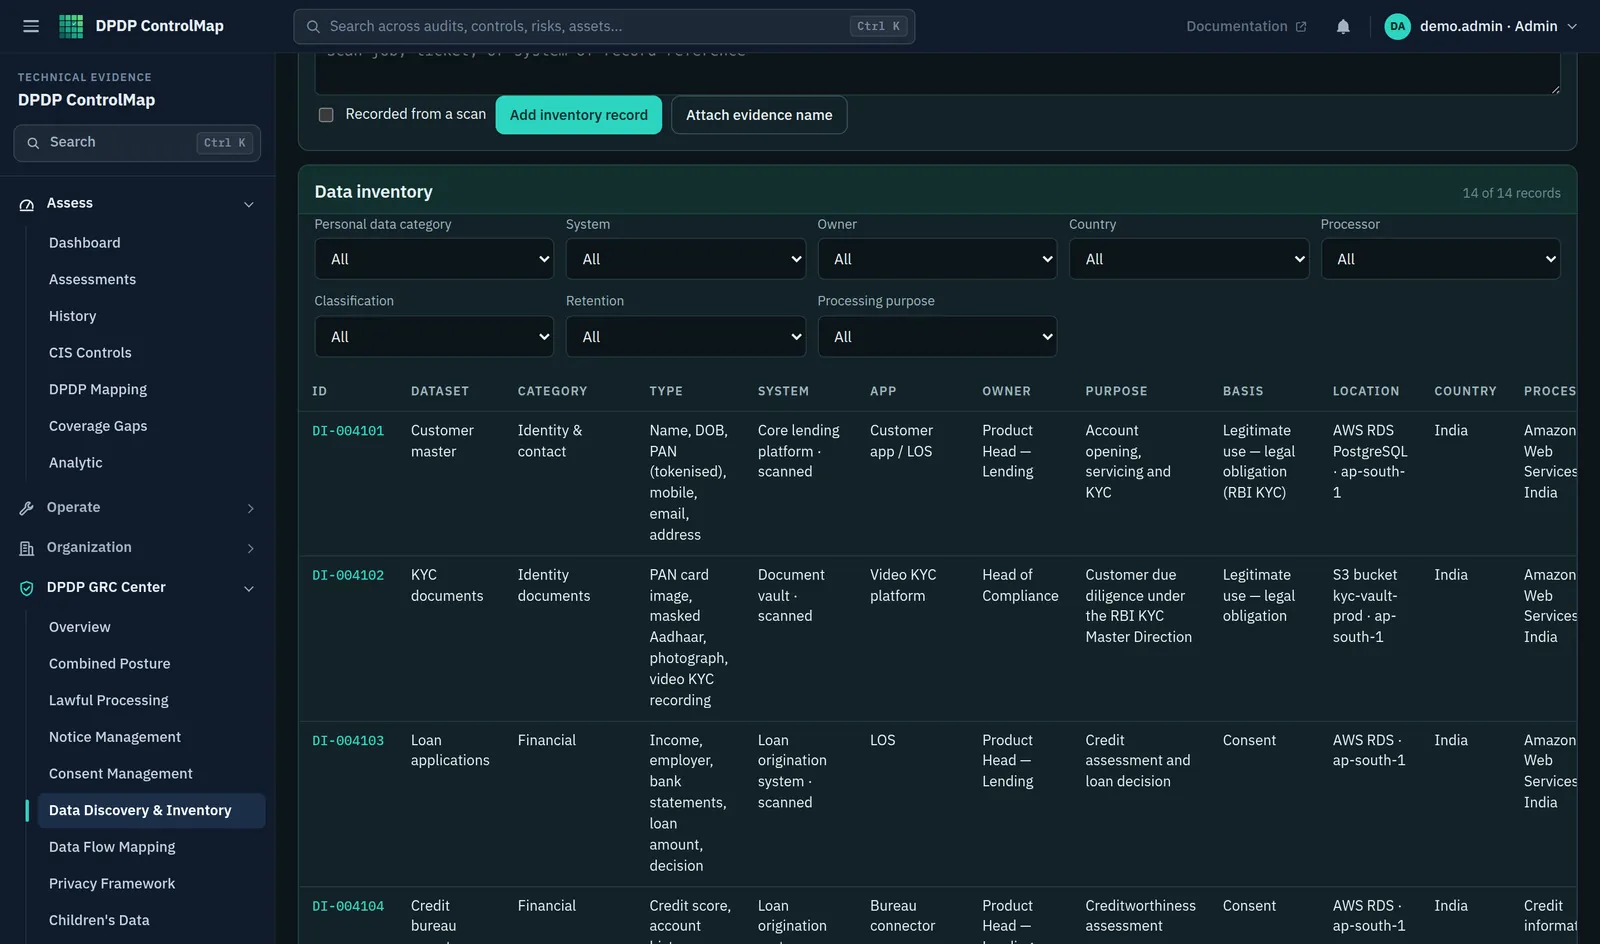
Data Discovery
Establish which systems hold personal data and how much is still unknown.
Data Inventory
One register of datasets, owners, purposes, locations and retention.
Data Classification
Label personal, children's, confidential and restricted data consistently.
Data Mapping
Draw how personal data moves from source to destination.
Data Flow Management
Review each flow for owner, basis, processor and country.
Records of Processing
Keep processing activities documented with purpose and lawful basis.
BModule group
Privacy Operations
The duties that Data Principals experience directly. Each is run as a process with stages, owners and a record of what was done.
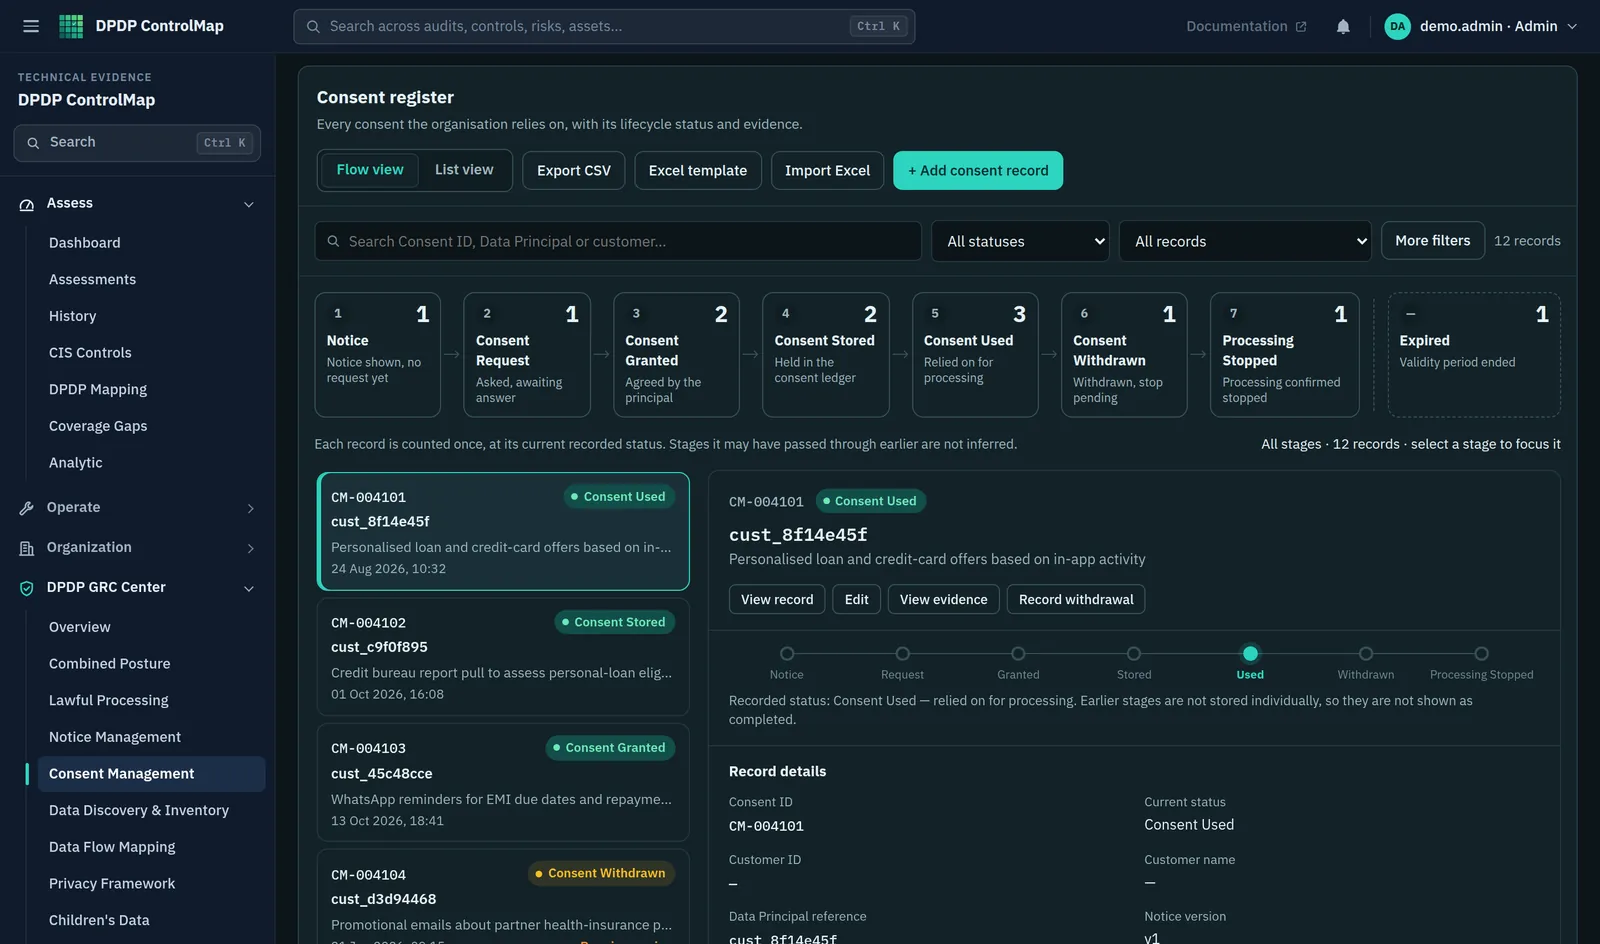
Consent Management
Follow consent from notice and grant through withdrawal and stop.
Privacy Notices
Version, review and publish notices against Section 5 and Rule 3.
Data Principal Rights
Handle access, correction, erasure, nomination and grievance requests.
Consent Flows
The consent lifecycle shown stage by stage, from notice to processing stopped, with a count at each step.
Cookie Consent
A website banner that records a choice per purpose and holds back third-party scripts until it is granted.
Grievance Management
Grievances logged, owned and tracked against the period in Rule 14(3), in the same register as rights requests.
Children's Data
Record processing of children's data, how age is identified, how parental consent is verified and which safeguards apply.
CModule group
Compliance Management
The structure that turns the text of the Act and the Rules into assessed controls, scheduled reviews and a history of decisions.
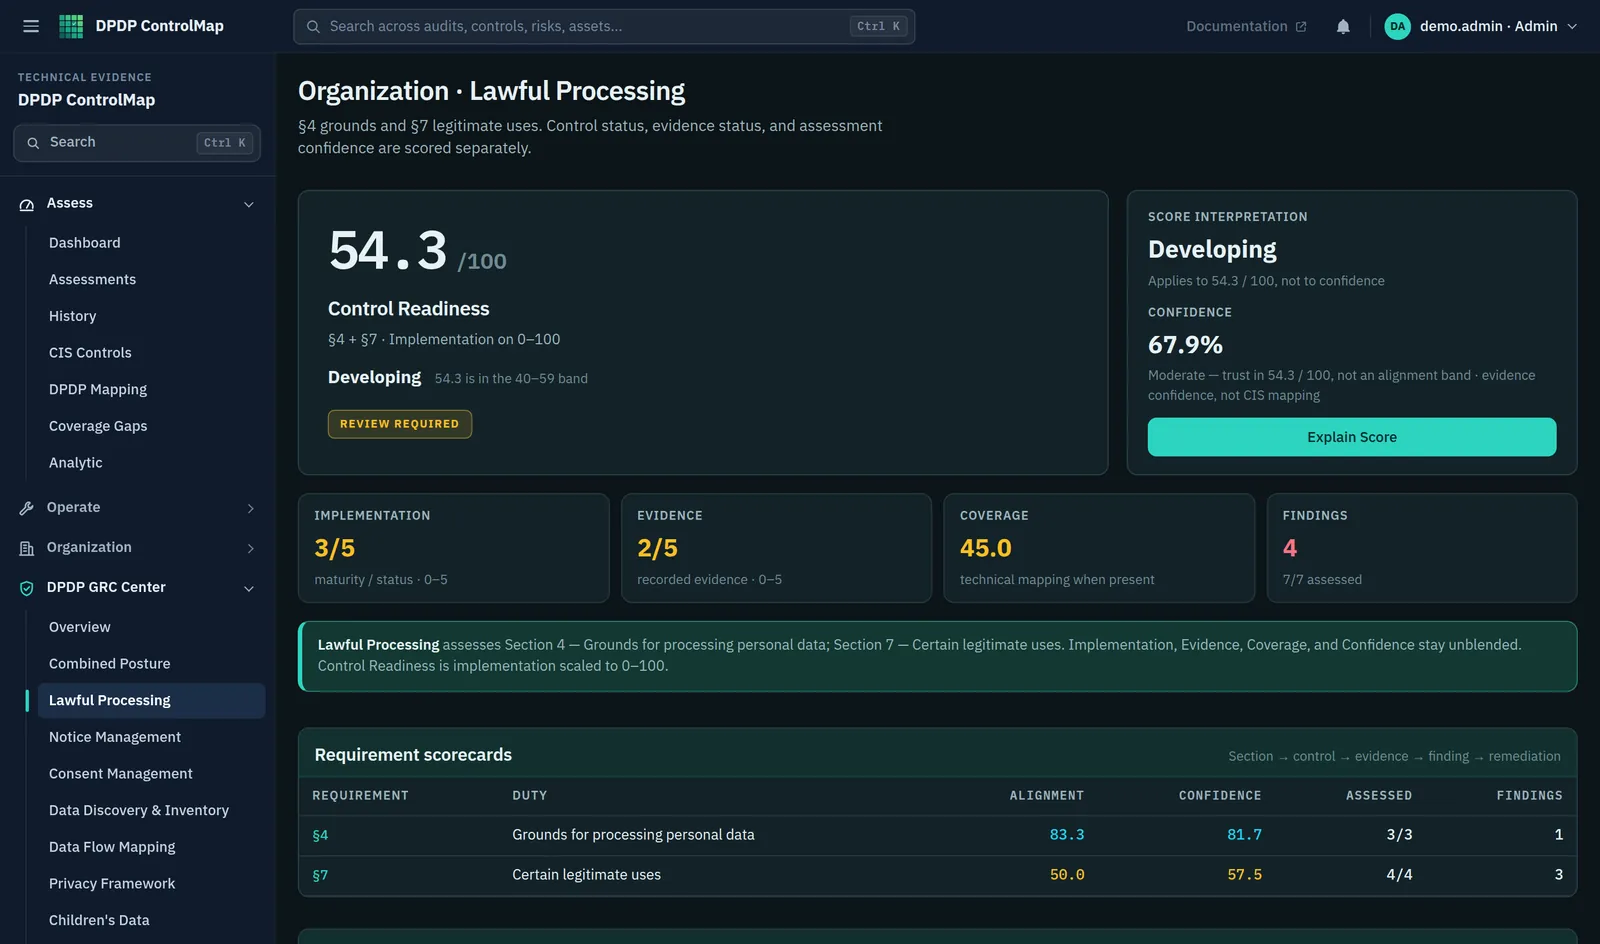
Audit Management
Assessments, evidence and an append-only record of who changed what.
DPIA
Schedule and evidence impact assessments for Significant Data Fiduciaries.
Policy Management
A policy register with owners, versions, approvals and review dates.
Compliance Notifications
In-app alerts for findings, overdue work and evidence that needs review.
DPDP Control Mapping
A catalogue of controls, each tied to the section or rule it comes from and the evidence that would support it.
Gap Assessment
The duties that technical scans cannot evidence, listed with the reason each needs a manual assessment.
DModule group
Security and Risk
Section 8 asks for reasonable security safeguards and makes the Data Fiduciary answerable for its processors. These modules track both.
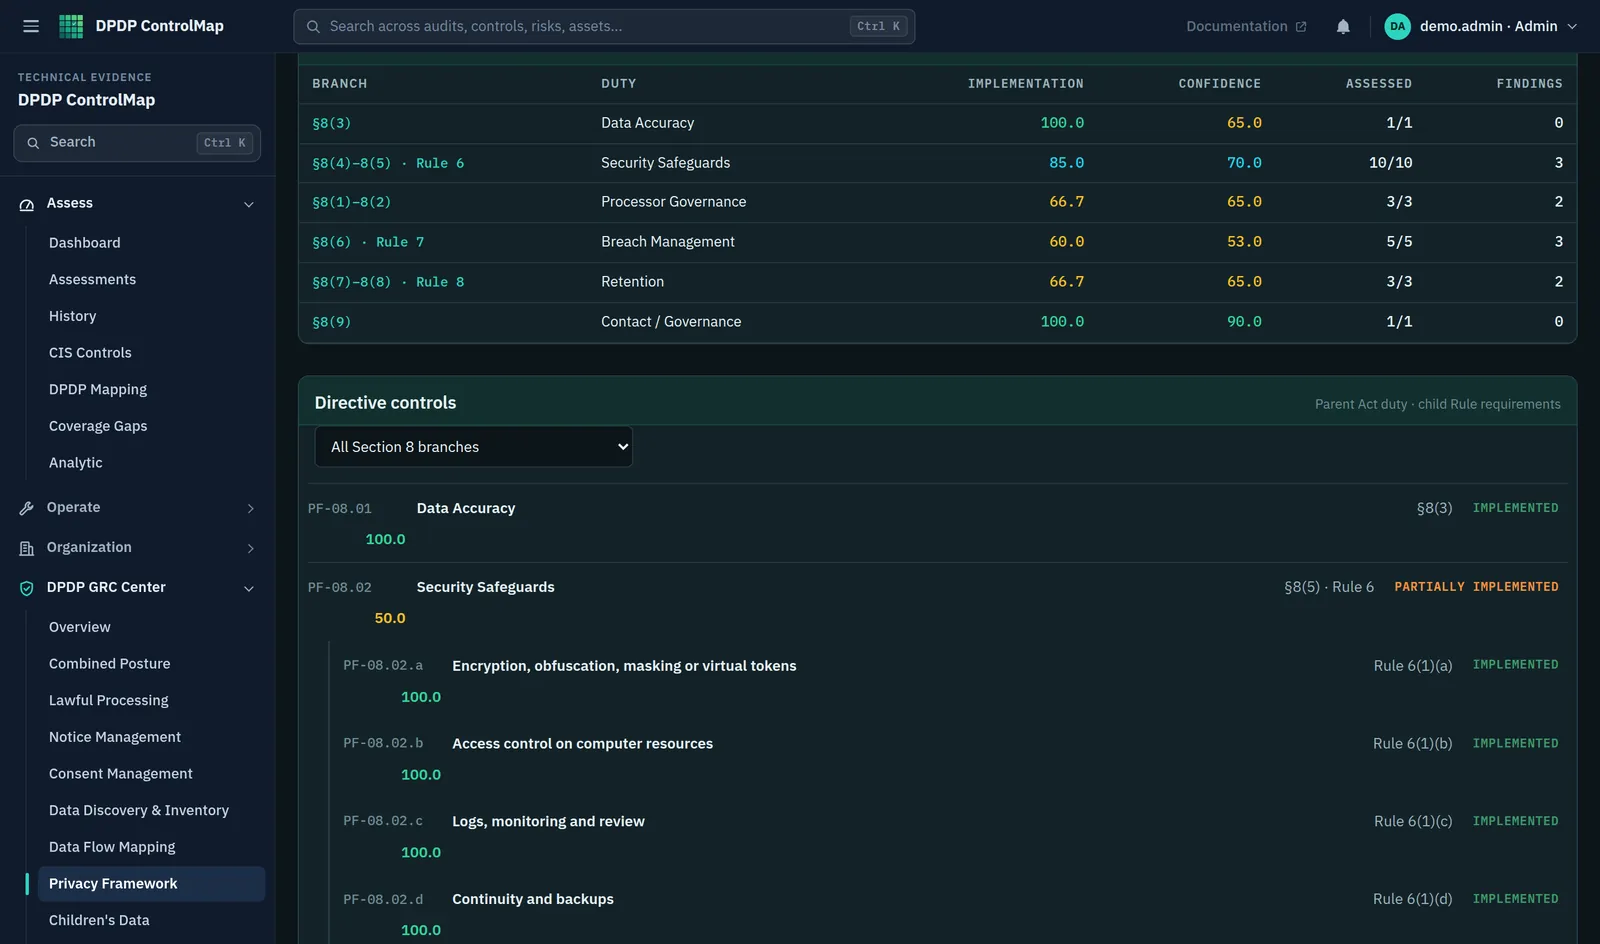
Breach Management
Readiness controls and a log for personal data breaches.
Processor Oversight
Keep Data Processors, contracts and their safeguards in view.
Incident Response
Each incident followed from detection through containment and intimation to closure, with a recorded root cause.
Risk Assessment
A risk register with likelihood and impact scoring, inherent and residual ratings, appetite thresholds and treatment.
Technical Readiness
Configuration checks from CIS benchmark assessments and Wazuh, mapped to the security safeguards in Rule 6.
EModule group
Reporting and Intelligence
What management, auditors and the board ask to see. These capabilities are part of the platform and draw on every other module.
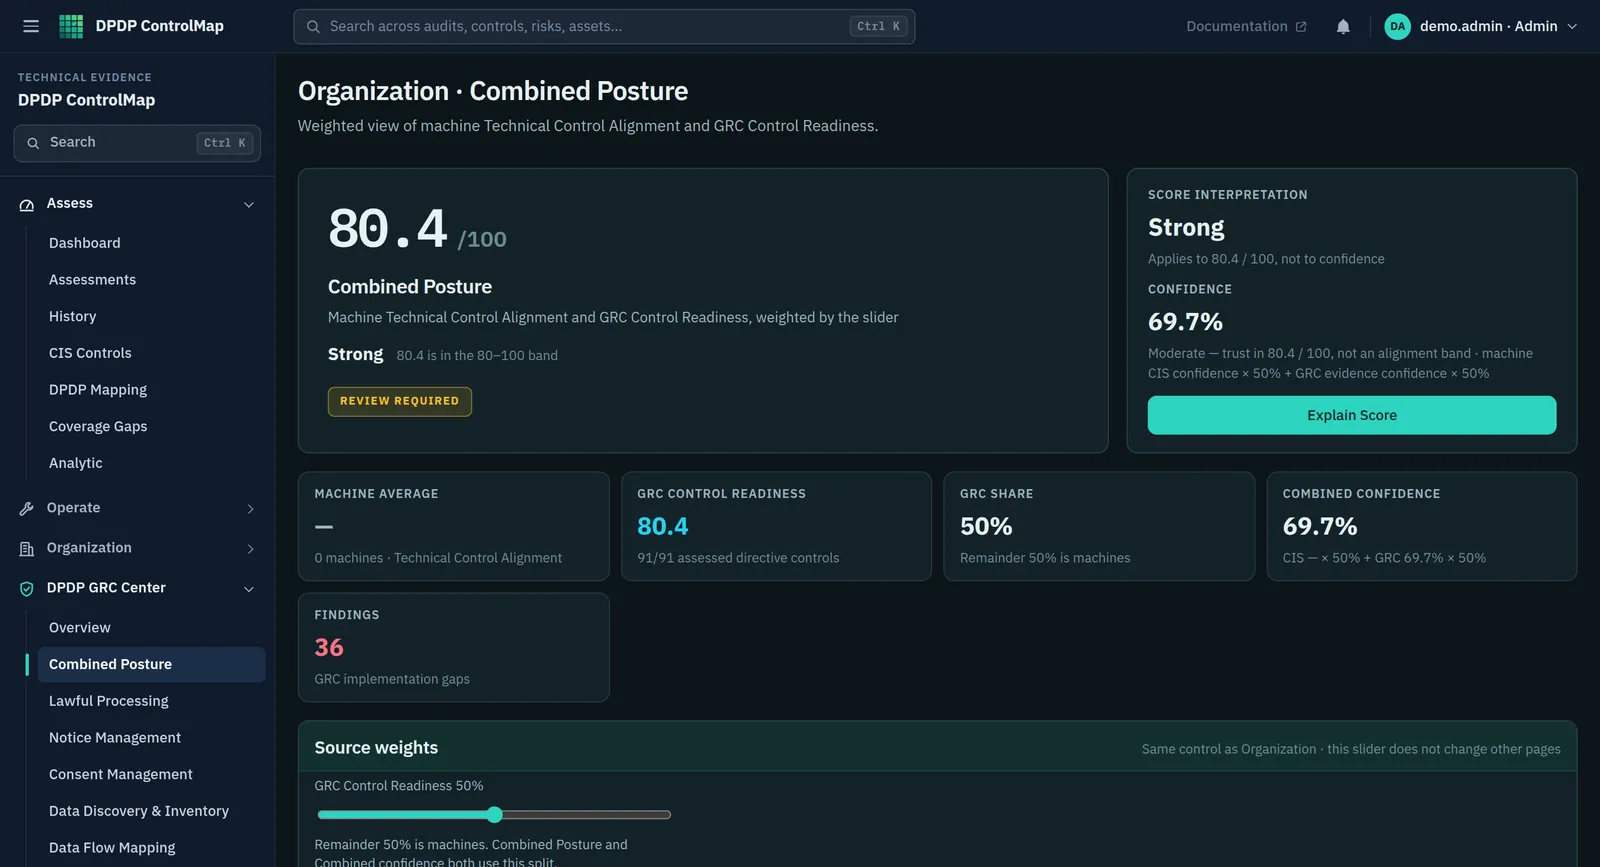
Compliance Dashboard
Control readiness for each module, with implementation, evidence and confidence reported as separate figures.
Management Visibility
One view that sets technical control alignment beside governance readiness, with the weighting between them shown.
Compliance Reports
PDF reports of technical readiness: executive, technical, control evidence, remediation and coverage gap.
Audit Evidence
An evidence report for auditors, and an append-only log of who changed what and when.
Remediation Tracking
Findings turned into remediation items with an owner, a due date and a status, ordered by severity.
Posture History
How readiness has moved between stored assessments, so progress is shown and not asserted.
Build a clearer path to DPDP readiness.
See how ControlMap brings your data inventory, obligations, evidence and remediation into one working record.